Don’t panic: How Gulf energy sector is training for cyber crisis
Gulf oil and gas shifts from box-ticking to consequence-driven cyber resilience
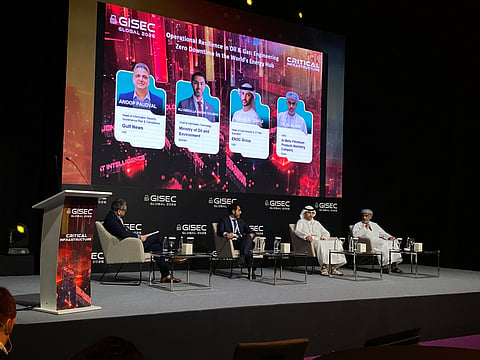
Cyber security leaders warned that oil and gas operators are at a heightened risk amid digitalisation and IOT, OT convergence, urging to start focusing more on consequence-driven resilience than compliance.
This was discussed at a panel discussion on operational resilience in oil and gas on the first day of GISEC Global 2026, where opening remarks underscored a 45 per cent surge in attacks on OT and IoT devices and ransomware disruptions impacting over 30 per cent of global utilities.
Ali Abdulla Hasan Salman, Chief of information technology at Ministry of Oil and Environment in Bahrain, highlighted the importance of this discussion by underscoring that the oil and gas sector is not just another industry, but the engine room of the entire economy.
“Once it is disrupted, the whole ecosystem is affected,” he says, pointing to the importance of comprehensive incident response plans and cyber resilience programmes. That is something the whole panel agreed on, including Khaled Al Teneiji, Cyber Security Head at ENOC, Talal Alasmi, CISO at Al Maha Petroleum Products Marketing Co. SAOG in Oman, and Anoop Paudval, Head of Information Security and GRC at Gulf News.
On the motives of these attacks Salman stated that this could be of financial and state interest to target the energy sector.
Early warning detection
Khaled Al Teneiji pushed back on the framing of threats as “IT versus OT”, arguing instead that what is smarter is for organisations to: “map their own possible consequences into their business processes, either it is coming from an IT or OT, or even integrated as a threat. So, the threat vectors can map from an IT to OT to create a kinetic impact,” he said.
In practice, that means security and operations teams planning together, so a fix on one side never creates a problem on the other.
The clearest solution the panel offered was full visibility. Knowing exactly what is running, where, and how it is behaving is the single biggest lever for staying ahead of threats.
“Accuracy of an asset inventory decays unless continuously maintained,” Al Teneiji expressed pointing to the company’s need to move from box-ticking compliance to active, live monitoring.
Salman agreed, pointing to full visibility, including hardware, software, APIs, certificates and OT controller behaviour as the industry’s real early warning system.
When it happens, don’t panic
If you ask the panel, it is not a question of if an attack hits, but when. That is why they stress preparation.
Alasmi called for tested company-wide continuity and response plans, built on clear recovery targets, so teams know exactly what to do the moment something breaks.
Salman went further, stressing the human factor: “There is something they call psychological safety today. How you train people working under pressure. How you train people working under crisis, under incidents. It is not a one-time job. It needs to be practised before an incident several times,” he said.
Al Teneiji expressed that security teams need to sit down with process engineers before disaster strikes. “The way you talk to an IT engineer is totally different from a process engineer. That cultural element is very important for the security experts to go and try to map between them. During response, you need those engineers to be with you to identify and make the right judgement,” he said.


